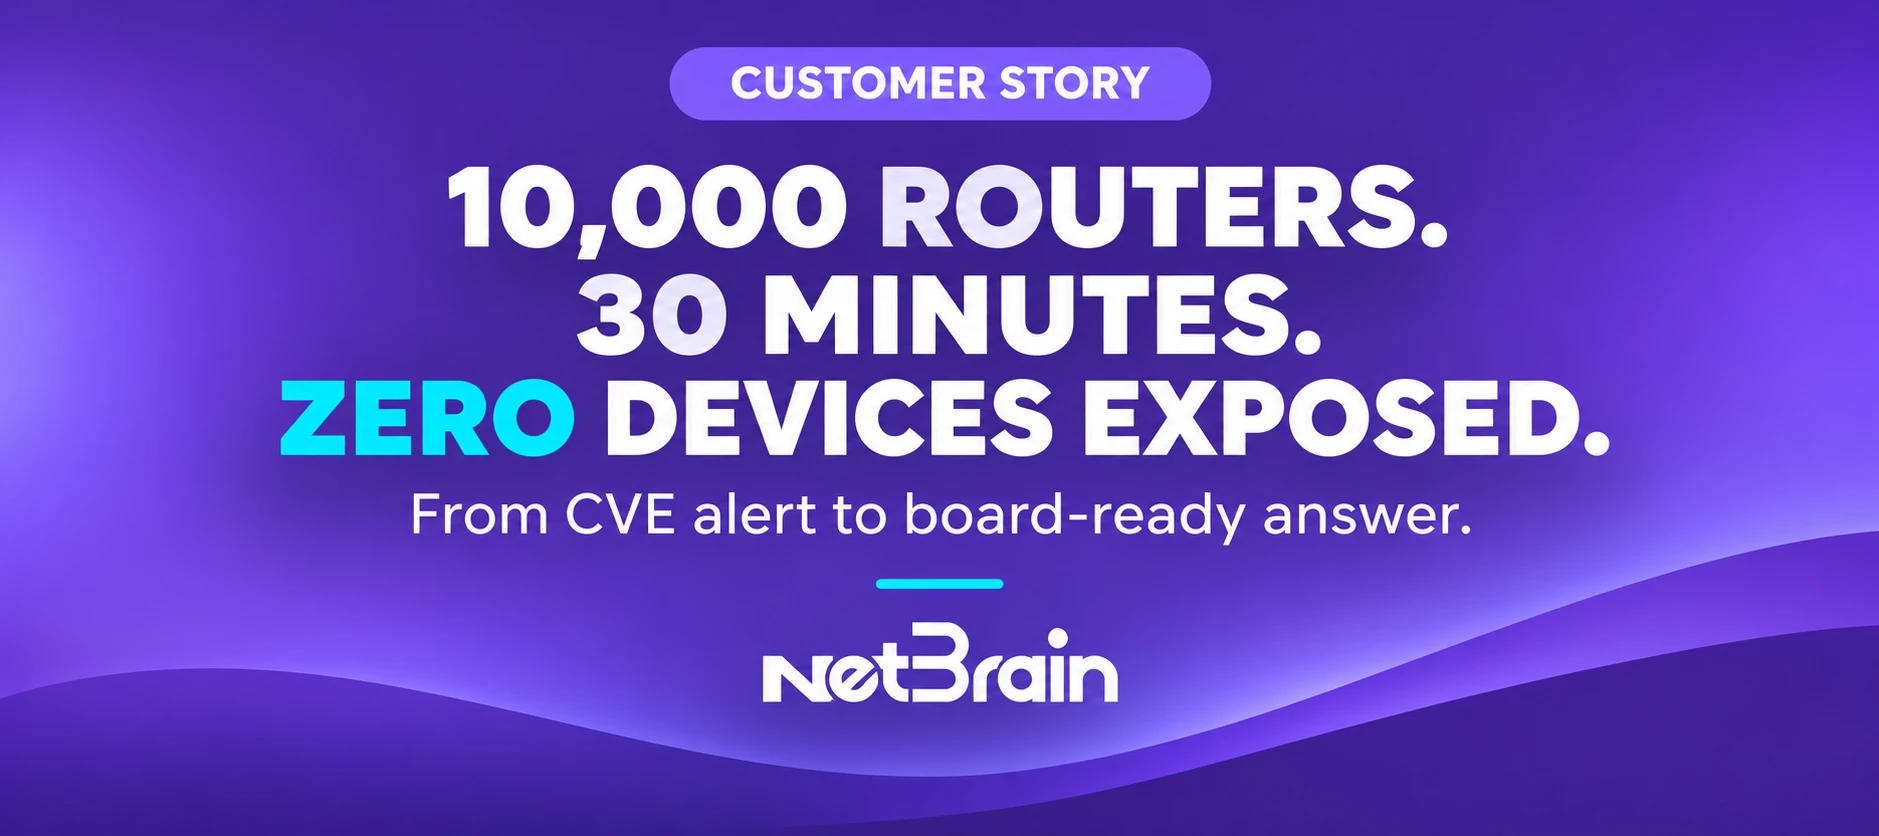
After a CISA-listed Known Exploited Vulnerability (KEV) alert, a global energy utility used NetBrain to assess approximately 10,000 routers and determine which devices actually needed attention.
The results:
-
10,000 routers assessed
-
30 minutes to reach a configuration-level answer
-
Approximately 100 routers identified for cleanup
-
Zero devices exposed to the internet
By leveraging its existing NetBrain deployment, the security team was able to replace manual device-by-device investigation with an evidence-backed response.
Fewer devices to chase. More time to design.
A new CVE shouldn't mean starting another lengthy manual investigation. NetBrain helps your team focus remediation on real exposure, rather than long affected-device lists, so your engineers can spend more time on proactive network operations, design, and architecture.
Explore NetBrain CVE Assessment
Join the conversation
How does your team currently assess and respond to new CVEs? Are you relying on version-based vulnerability scans, manual configuration checks, or automation?
Share your experiences and challenges in the comments below!